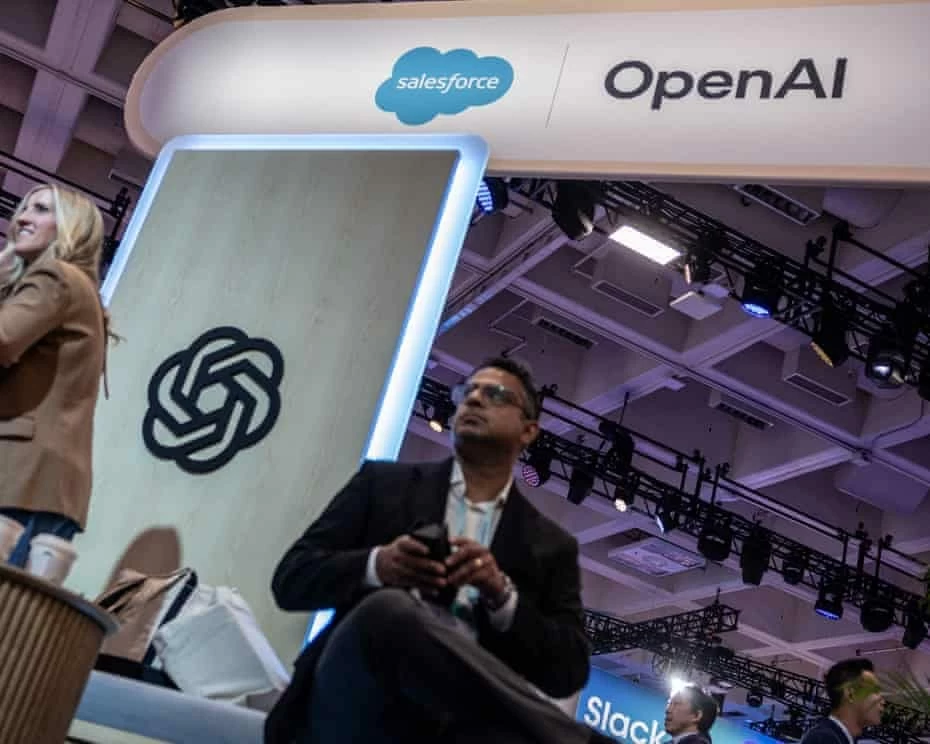
تمكن باحثون في الأمن السيبراني من استغلال ثغرة في بيئة تابعة لشركة OpenAI، والوصول إلى حسابات مرتبطة بموظفين في الشركة، مستعينين بأداة الذكاء الاصطناعي «Claude» التابعة لشركة Anthropic، في واقعة تكشف تنامي قدرة أدوات الذكاء الاصطناعي على تسريع تنفيذ هجمات إلكترونية معقدة.
ووفق بحث أجرته شركة الأمن السيبراني الناشئة Hacktron AI، بدأ الباحثون العملية باستخدام «Claude» للمساعدة في إنتاج الأكواد اللازمة لتنفيذ مراحل من الهجوم، قبل الوصول إلى بيئة مرتبطة بخدمات OpenAI. وحصلت الشركة لاحقاً على مكافأة قدرها 6500 دولار من OpenAI بعد إبلاغها بالثغرة ضمن برنامج مكافآت اكتشاف الأخطاء الأمنية.
ثغرة في منتدى داخلي
بدأت العملية باستغلال ثغرة مرتبطة بمنتدى داخلي لموظفي OpenAI مستضاف على منصة Discourse، ما أتاح للباحثين الوصول إلى حسابات ChatGPT مرتبطة بعدد من موظفي الشركة.
وبمساعدة «Claude»، تمكن الفريق من تطوير الأكواد اللازمة لتنفيذ مراحل من العملية، ثم اختبار الوصول إلى خدمة تابعة لـOpenAI من خلال مستودع على منصة GitHub باستخدام آلية «Pull Request»، التي تتيح اقتراح تعديلات على الملفات البرمجية.
وأكدت Hacktron أن الاختبار جرى ضمن برنامج OpenAI المخصص للباحثين الأمنيين، وأنها أبلغت الشركة بالثغرة بعد إثبات إمكانية استغلالها.
وأوضح الباحثون أنهم تمكنوا من الوصول إلى الكود الموجود في المستودع، لكنهم لم يقوموا بتنزيله أو نسخ بيانات حساسة، واستخدموا التعديل البرمجي دليلاً على نجاح الوصول إلى البيئة الداخلية.
نطاق وصول واسع
وأشارت Hacktron إلى أن نطاق الوصول المحتمل عبر الثغرة كان واسعاً، خصوصاً مع إمكانية ارتباط حسابات ChatGPT وCodex بخدمات وأدوات أخرى تستخدمها المؤسسات.
وأظهرت العملية، التي نُفذت خلال فترة قصيرة، كيف يمكن للذكاء الاصطناعي تقليص الوقت والخبرة اللازمين لتحويل ثغرات تقنية إلى هجمات قابلة للتنفيذ.
وبحسب الشركة، فإن مهام كانت تتطلب سابقاً فريقاً متخصصاً وموارد كبيرة وأشهرًا من العمل، بات من الممكن إنجازها خلال أيام بمساعدة أدوات الذكاء الاصطناعي.
وحصلت Hacktron على 6500 دولار من OpenAI مقابل اكتشاف الثغرة والإبلاغ عنها.
عالجنا الثغرات: OpenAI
من جانبها، شكرت OpenAI الباحثين على إبلاغها بالثغرات ومشاركة نتائج الاختبار، مؤكدة اتخاذ الإجراءات اللازمة لمعالجة نقاط الضعف التي استُغلت خلال العملية.
وتأتي الواقعة وسط تزايد النقاش حول استخدام الذكاء الاصطناعي في تنفيذ هجمات إلكترونية أكثر تعقيداً، مع تطور قدرات النماذج في كتابة الأكواد وتحليل الأنظمة وأتمتة مراحل متعددة من العمليات التقنية.
جدل حول سرعة تطوير الذكاء الاصطناعي
وتزامنت الواقعة مع تصاعد النقاش داخل قطاع التكنولوجيا حول سرعة تطور أنظمة الذكاء الاصطناعي المتقدمة.
وكان الرئيس التنفيذي لشركة Anthropic، داريو أمودي، قد دعا إلى إبطاء وتيرة تطوير الذكاء الاصطناعي المتقدم، مع تعزيز إجراءات السلامة والتقييم المستقل. وحظيت دعوته بتأييد الرئيس التنفيذي لـOpenAI سام ألتمان، والرئيس التنفيذي لـGoogle DeepMind ديميس هاسابيس، وإيلون ماسك.
في المقابل، يبرز خلاف داخل قطاع التكنولوجيا بشأن كيفية التعامل مع هذه المخاطر؛ إذ يرى مؤيدو تشديد إجراءات السلامة ضرورة مواكبة التطور بإجراءات رقابية وتقييمات مستقلة، بينما يحذر منتقدون من أن القيود قد تؤثر في الابتكار والمنافسة.
ترمب: لا نريد التخلي عن الصدارة
وفي السياق نفسه، رفض الرئيس الأمريكي دونالد ترمب الدعوات إلى إبطاء تطوير الذكاء الاصطناعي، مؤكداً خلال وجوده في أيرلندا ضرورة حفاظ الولايات المتحدة على ريادتها في هذا المجال، في ظل المنافسة مع الصين.
وقال ترمب إن الولايات المتحدة «تقود الصين في الذكاء الاصطناعي»، وإنه يريد الحفاظ على ذلك، مشيراً في الوقت نفسه إلى إمكانية وضع ضوابط، لكنه وصف بعض التحذيرات بشأن مستقبل الذكاء الاصطناعي بأنها مبالغ فيها.
Cybersecurity researchers managed to exploit a vulnerability in an environment belonging to OpenAI, gaining access to accounts linked to employees at the company, using the AI tool "Claude" from Anthropic. This incident reveals the growing capability of AI tools to accelerate the execution of complex cyberattacks.
According to research conducted by the emerging cybersecurity company Hacktron AI, the researchers began the process by using "Claude" to help produce the necessary codes to execute stages of the attack, before accessing an environment linked to OpenAI services. The company later received a $6,500 reward from OpenAI after reporting the vulnerability as part of its security bug bounty program.
Vulnerability in an Internal Forum
The process began by exploiting a vulnerability related to an internal forum for OpenAI employees hosted on the Discourse platform, which allowed the researchers to access ChatGPT accounts linked to several company employees.
With the help of "Claude," the team was able to develop the necessary codes to execute stages of the process, and then test access to an OpenAI service through a repository on GitHub using a "Pull Request" mechanism, which allows for suggesting modifications to code files.
Hacktron confirmed that the testing was conducted within OpenAI's program dedicated to security researchers, and that they reported the vulnerability to the company after proving its exploitability.
The researchers explained that they were able to access the code in the repository, but they did not download it or copy sensitive data, using the code modification as evidence of successful access to the internal environment.
Wide Access Scope
Hacktron noted that the potential access scope through the vulnerability was wide, especially with the possibility of linking ChatGPT and Codex accounts to other services and tools used by organizations.
The operation, which was executed in a short period, demonstrated how AI can reduce the time and expertise required to turn technical vulnerabilities into executable attacks.
According to the company, tasks that previously required a specialized team and significant resources and months of work can now be completed in days with the help of AI tools.
Hacktron received $6,500 from OpenAI for discovering and reporting the vulnerability.
We Addressed the Vulnerabilities: OpenAI
For its part, OpenAI thanked the researchers for reporting the vulnerabilities and sharing the test results, confirming that necessary actions were taken to address the weaknesses exploited during the process.
This incident comes amid increasing discussions about the use of AI in executing more complex cyberattacks, as the capabilities of models in writing code, analyzing systems, and automating multiple stages of technical processes evolve.
Debate Over the Speed of AI Development
The incident coincided with rising discussions within the tech sector regarding the rapid development of advanced AI systems.
Anthropic's CEO, Dario Amodei, had called for slowing down the pace of advanced AI development while enhancing safety measures and independent assessments. His call received support from OpenAI CEO Sam Altman, Google DeepMind CEO Demis Hassabis, and Elon Musk.
In contrast, a disagreement is emerging within the tech sector on how to handle these risks; proponents of tightening safety measures argue for keeping pace with development through regulatory measures and independent evaluations, while critics warn that restrictions could impact innovation and competition.
Trump: We Don't Want to Give Up Our Lead
In this context, U.S. President Donald Trump rejected calls to slow down AI development, emphasizing during his visit to Ireland the need for the United States to maintain its leadership in this field amid competition with China.
Trump stated that the U.S. "leads China in AI," and he wants to keep it that way, while also indicating the possibility of implementing controls, but he described some warnings about the future of AI as exaggerated.