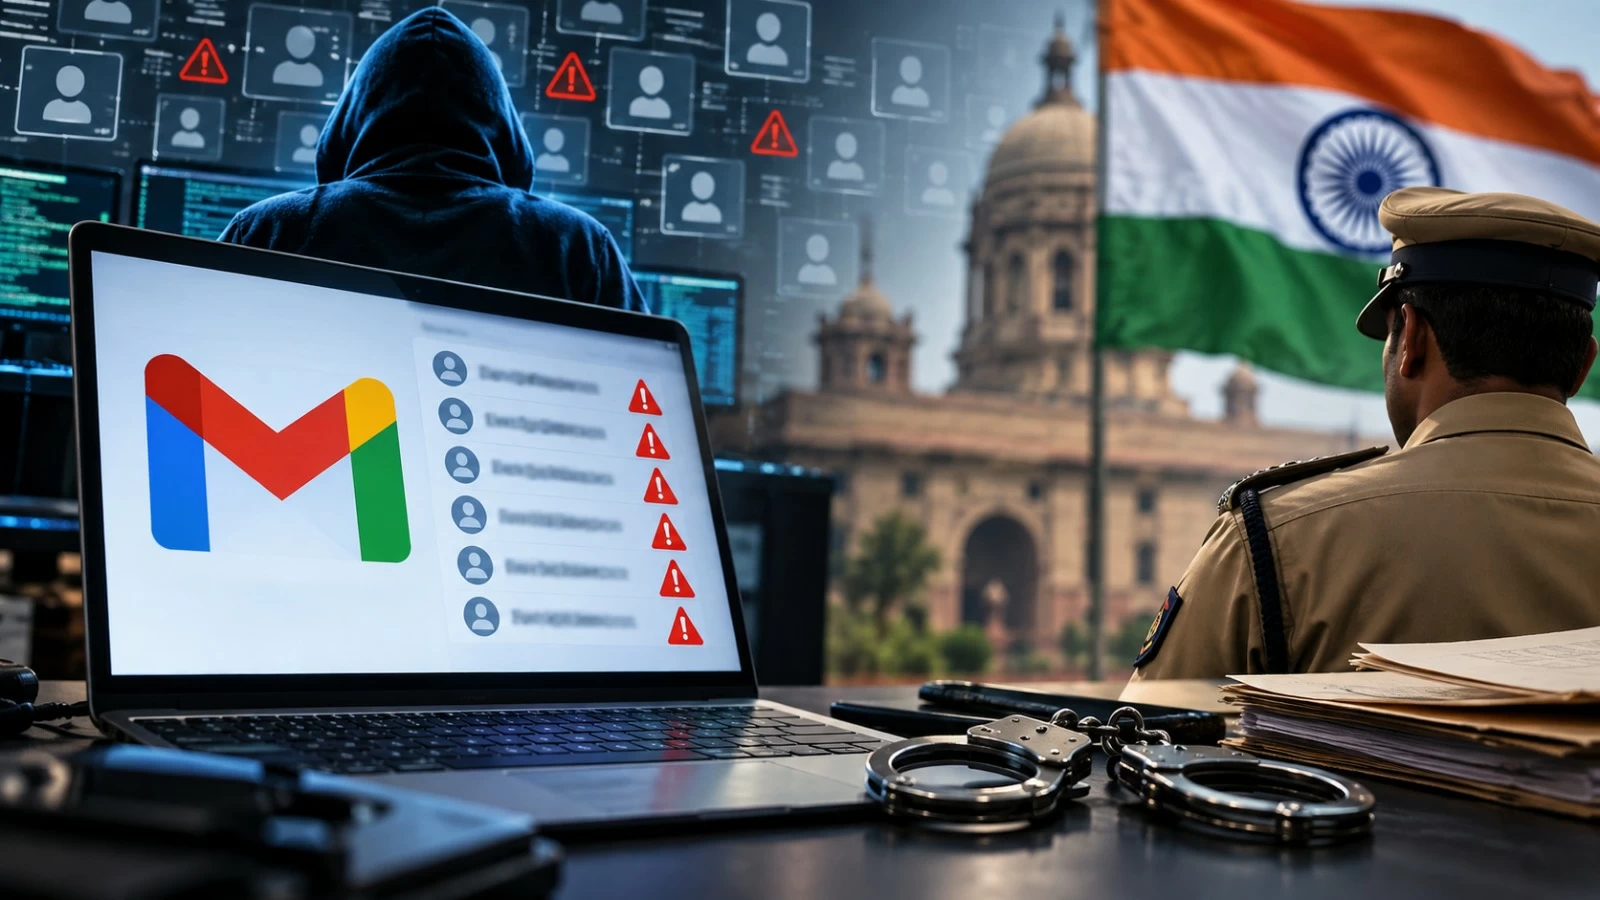
تعتزم الشرطة الهندية مساءلة شركة «قوقل» بشأن إجراءات الحماية في خدمة Gmail، بعد تفكيك شبكة إجرامية أنشأت وأدارت أكثر من نصف مليون حساب مزيف، استُخدم بعضها في إرسال تهديدات كاذبة بوجود قنابل إلى مكاتب حكومية.
وكشفت شرطة ولاية غوجارات غربي الهند، عن ضبط 513,847 حساب Gmail وكلمات مرور مرتبطة بها، قالت إنها كانت مستخدمة منذ عام 2022، فيما ألقت القبض على شخصين على خلفية القضية.
وقال مسؤول بارز في مكافحة الجرائم الإلكترونية بشرطة غوجارات، إن حجم الحسابات المزيفة المكتشفة غير مسبوق، مشيراً إلى أن السلطات تعتزم مخاطبة «قوقل» للمطالبة بإجراء تغييرات في سياساتها لمنع تجاوز إجراءات الحماية، كما تخطط لإدراج الشركة رسمياً ضمن نطاق التحقيق.
تهديدات كاذبة
وبدأ التحقيق بعد تلقي حكومة ولاية غوجارات رسالة عبر البريد الإلكتروني في 10 سبتمبر، تتضمن تهديداً بوجود قنبلة، قبل أيام من قمة مجموعة «بريكس» في نيودلهي، فيما أكدت الشرطة لاحقاً أن التهديدات كانت كاذبة.
وأفادت التحقيقات بأن أحد المقبوض عليهما كان على اتصال بمشترٍ في بنغلاديش، اشترى مجموعات من الحسابات ودفع جزءاً من قيمتها باستخدام العملات المشفرة لإرسال رسائل البريد الإلكتروني المزيفة.
المصادقة الثنائية تثير التساؤلات
وأثار استخدام الحسابات الاحتيالية لميزة المصادقة الثنائية مخاوف المحققين، كونها إحدى وسائل الحماية الإضافية التي توفرها «قوقل» للمستخدمين، فيما تحقق السلطات في كيفية تمكن الشبكة من إنشاء وإدارة هذا العدد الكبير من الحسابات وتجاوز إجراءات الحماية.
ولم ترد «قوقل»، المملوكة لشركة «ألفابت»، على طلب للتعليق حتى وقت نشر تقرير «رويترز»، كما لم يتضح ما إذا كانت الشركة قد تواجه اتهامات أو عقوبات قانونية على خلفية التحقيق.
The Indian police intend to question Google regarding the security measures in the Gmail service, after dismantling a criminal network that created and managed more than half a million fake accounts, some of which were used to send false bomb threat emails to government offices.
The police in the western Indian state of Gujarat revealed that they had seized 513,847 Gmail accounts and their associated passwords, which they said had been in use since 2022, while two individuals were arrested in connection with the case.
A senior official in the cybercrime unit of the Gujarat police stated that the scale of the discovered fake accounts is unprecedented, noting that authorities plan to address Google to demand changes in its policies to prevent security measures from being bypassed, and they also plan to officially include the company in the scope of the investigation.
False Threats
The investigation began after the Gujarat state government received an email on September 10, containing a bomb threat, just days before the BRICS summit in New Delhi, while police later confirmed that the threats were false.
Investigations revealed that one of the arrested individuals was in contact with a buyer in Bangladesh, who purchased batches of accounts and paid part of their value using cryptocurrencies to send the fake emails.
Two-Factor Authentication Raises Questions
The use of fraudulent accounts for two-factor authentication has raised concerns among investigators, as it is one of the additional security measures provided by Google to users, while authorities are investigating how the network was able to create and manage such a large number of accounts and bypass security measures.
Google, owned by Alphabet, did not respond to a request for comment by the time Reuters published the report, and it remains unclear whether the company will face any charges or legal penalties as a result of the investigation.