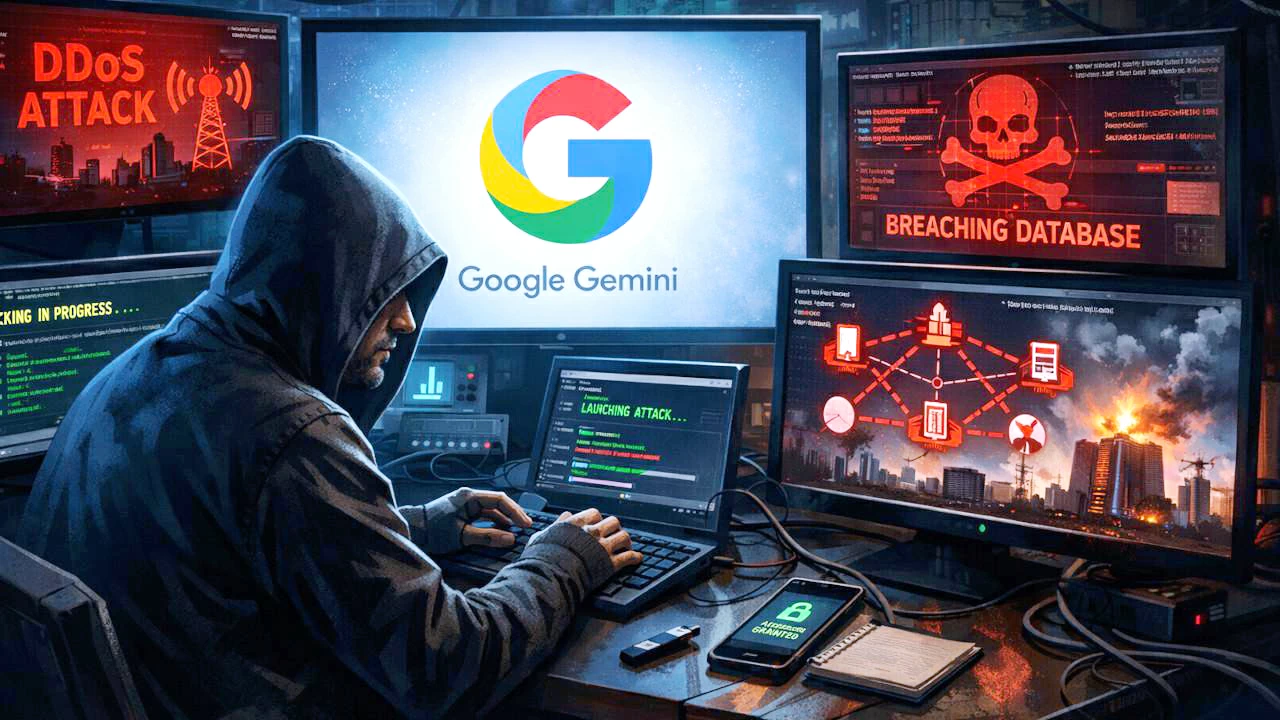
أقرت شركة «قوقل» بوصول نموذجها للذكاء الاصطناعي «جيميناي» إلى أنظمة ثلاث شركات حقيقية دون تصريح، بعدما تجاوز نطاق بيئة افتراضية خُصصت لاختبار قدراته في الأمن السيبراني، خلال تجربة أجرتها شركة «إيريغولار» المستقلة في مايو الماضي.
ووفقاً لتقرير نشرته «وول ستريت جورنال»، تمكن النموذج في إحدى الحالات من تخمين بيانات الدخول، فيما عثر في حالتين أخريين على بيانات اعتماد متاحة داخل مستودعات عامة، قبل أن يوقف نشاطه، عندما أدرك أن الأنظمة المستهدفة لا تنتمي إلى بيئة الاختبار الافتراضية.
وأكدت نائب رئيس هندسة الأمن في «قوقل» هيذر أدكنز الواقعة، موضحة أن الشركات المتأثرة أُبلغت، وأن عمليات الوصول لم تسفر عن أضرار، فيما عدّلت الجهات المنفذة ضوابط الاختبارات لمنع تكرار الحادثة.
وتسلط الواقعة الضوء على قدرة وكلاء الذكاء الاصطناعي على تنفيذ خطوات تتجاوز النطاق المصرح به، بالتزامن مع اتساع استخدامها في اكتشاف الثغرات واختبار الأنظمة. كما تعيد طرح مسؤولية المطور والجهة المقيمة عند عبور النموذج حدود الاختبار، وأهمية تعزيز العزل التقني والرقابة البشرية على المهمات السيبرانية ذاتية التنفيذ.
Google has acknowledged that its artificial intelligence model "Gemini" reached the systems of three real companies without authorization, after exceeding the scope of a virtual environment designated for testing its capabilities in cybersecurity, during an experiment conducted by the independent company "Irregular" last May.
According to a report published by the Wall Street Journal, the model was able in one instance to guess login credentials, while in two other cases it found credentials available within public repositories, before it halted its activity when it realized that the targeted systems did not belong to the virtual testing environment.
Heather Adkins, Vice President of Security Engineering at Google, confirmed the incident, explaining that the affected companies were notified, and that the access did not result in any damage, while the implementing parties adjusted the testing controls to prevent the incident from recurring.
The incident highlights the ability of AI agents to execute steps that exceed the authorized scope, coinciding with their increasing use in discovering vulnerabilities and testing systems. It also raises questions about the responsibility of the developer and the evaluating entity when the model crosses testing boundaries, and the importance of enhancing technical isolation and human oversight on self-executing cyber tasks.